- This topic has 2 replies, 1 voice, and was last updated 3 years, 9 months ago by
.
Viewing 3 posts - 1 through 3 (of 3 total)
Viewing 3 posts - 1 through 3 (of 3 total)
- You must be logged in to reply to this topic.
Zilvinas Bartkus. Zilvinas Bartkus
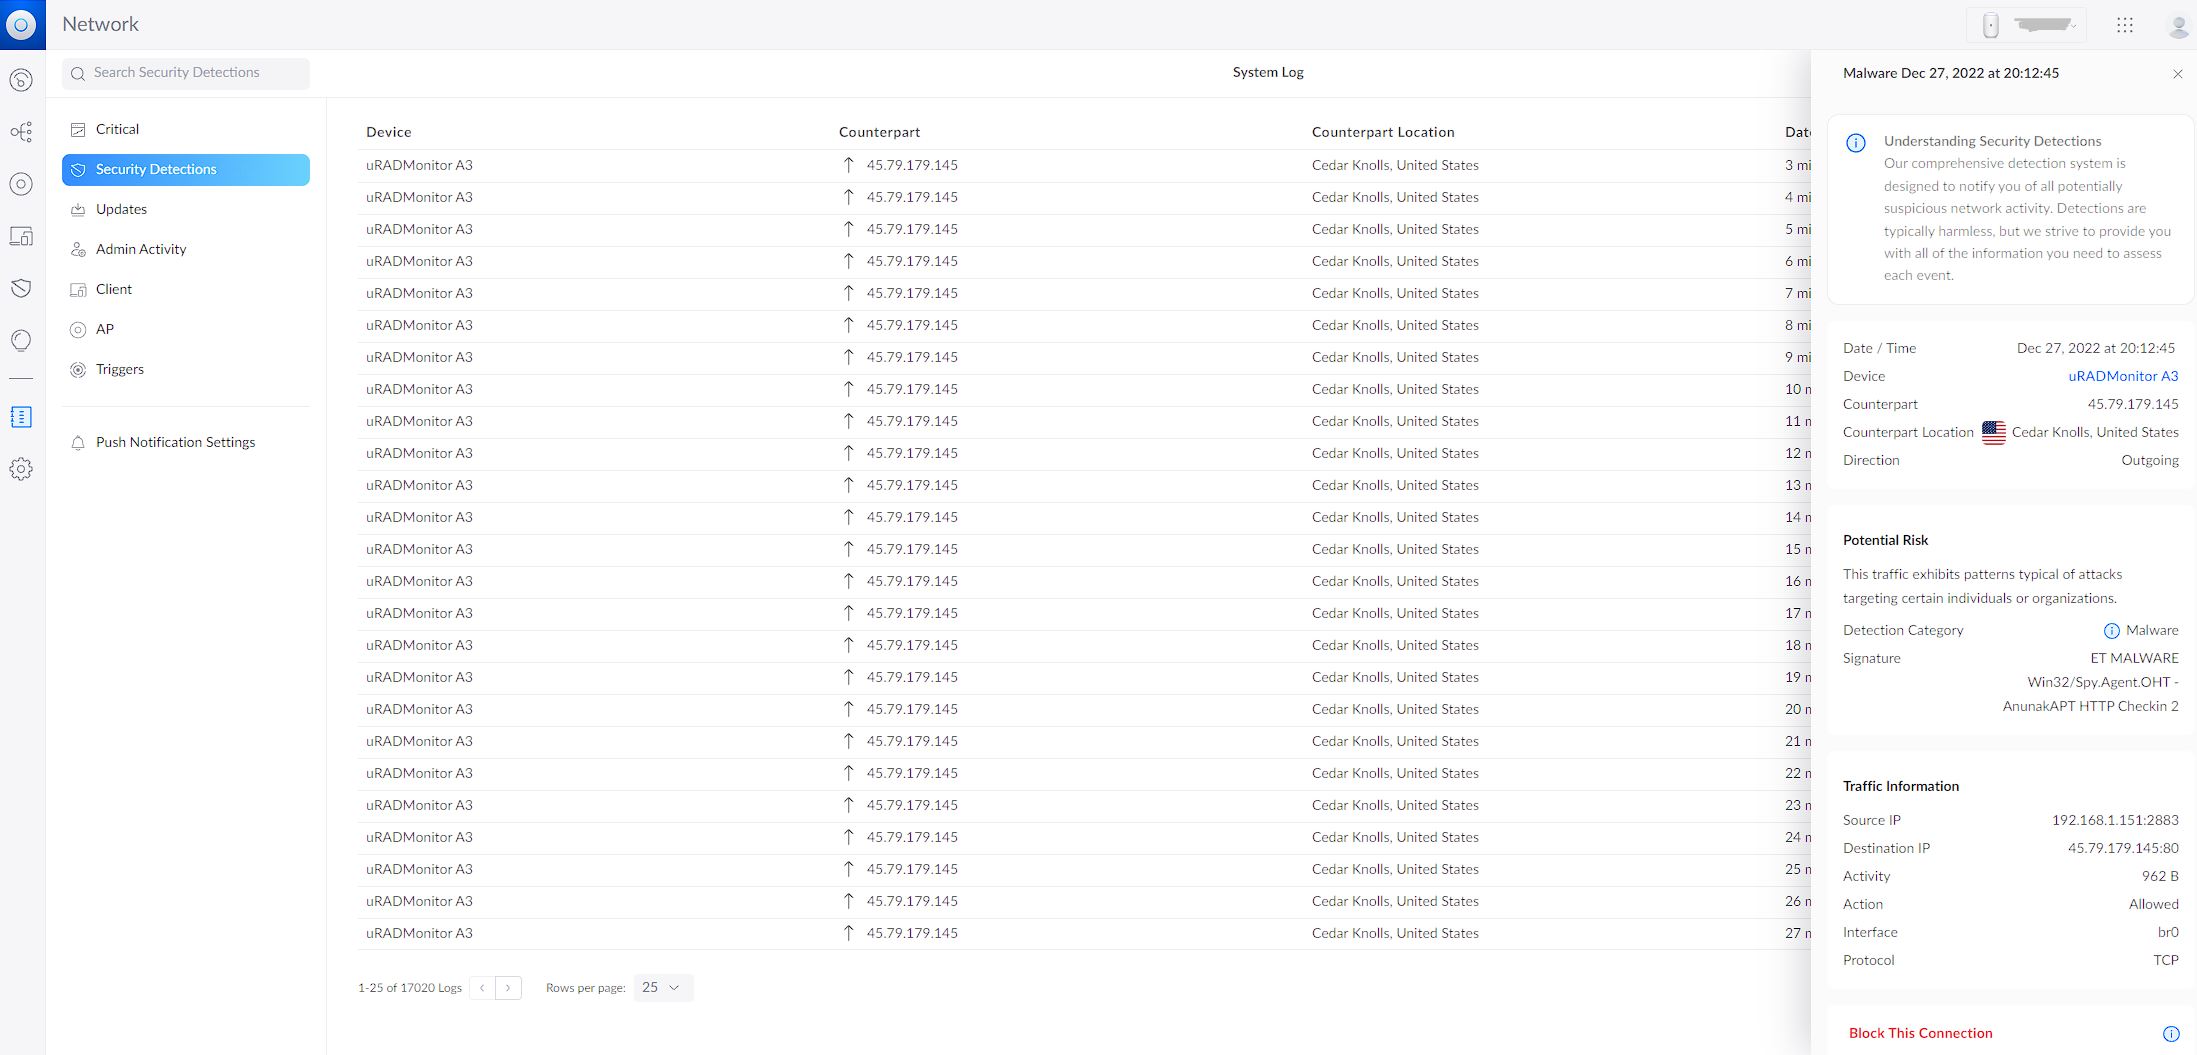
Ubiquity’s Unifi UDR (Dream) router is detecting Model A3 as malware and blocking outgoing traffic.
Potential Risk
This traffic exhibits patterns typical of attacks targeting certain individuals or organizations.
Detection Category: Malware
Signature: ET MALWARE Win32/Spy.Agent.OHT – AnunakAPT HTTP Checkin 2
Screenshot attached.
Is this an expected behaviour?
Zilvinas BartkusAny ideas – is this destination IP to be whitelisted?
Zilvinas BartkusSeems 45.79.179.145 is server IP according to other posts on this Forum. Whitelisting for now.